Research
Proof Without Identity
An age check needs one bit of information. Most of them ask for your whole ID.
So back in March, I presented my research, Proof Without Identity, at the Macksey Research Symposium at Johns Hopkins. Basically, why should a website need your name, your face or your birthday if all it needs to know is whether you’re over 18?
A Lockheed Martin Chief Architect and Technical Fellow has also reviewed and validated the research.
Johns Hopkins, March 2026.
The question is one bit
An age check only needs to answer one question: are you over 18 or not? That’s a yes or no answer.
But sites usually ask for a photo of your driver’s license, a selfie or a credit card number to get that answer. They collect all of that for a question that honestly didn’t need any of it, then a lot of the time just leave it stored somewhere after the check is done.
I kept seeing this in very different places. A system asks for way more information than it needs to answer the question and then holds onto it, so every one of those databases becomes another place that information can leak from. I wanted to figure out whether it actually had to work that way or whether people had just kept building these systems that way.
Who pays when it leaks
And when those systems leak, the people who had to hand over their information are the ones left dealing with it.
I used two examples in the talk. The first was in March 2023, when the Massachusetts Cannabis Control Commission accidentally included the names, home addresses, phone numbers and birthdates of current and former cannabis workers in its response to a public records request. Nobody even hacked anything – somebody just made a mistake. Then, in August 2025, a security researcher found two unprotected databases from an Ohio medical marijuana card company. Together they held 323 GB of data and nearly a million patient records, with Social Security numbers, driver’s license images and medical files.
Neither of those is an edge case. And as we all know, compliance requires data, the data piles up, and eventually the pile itself becomes the risk.
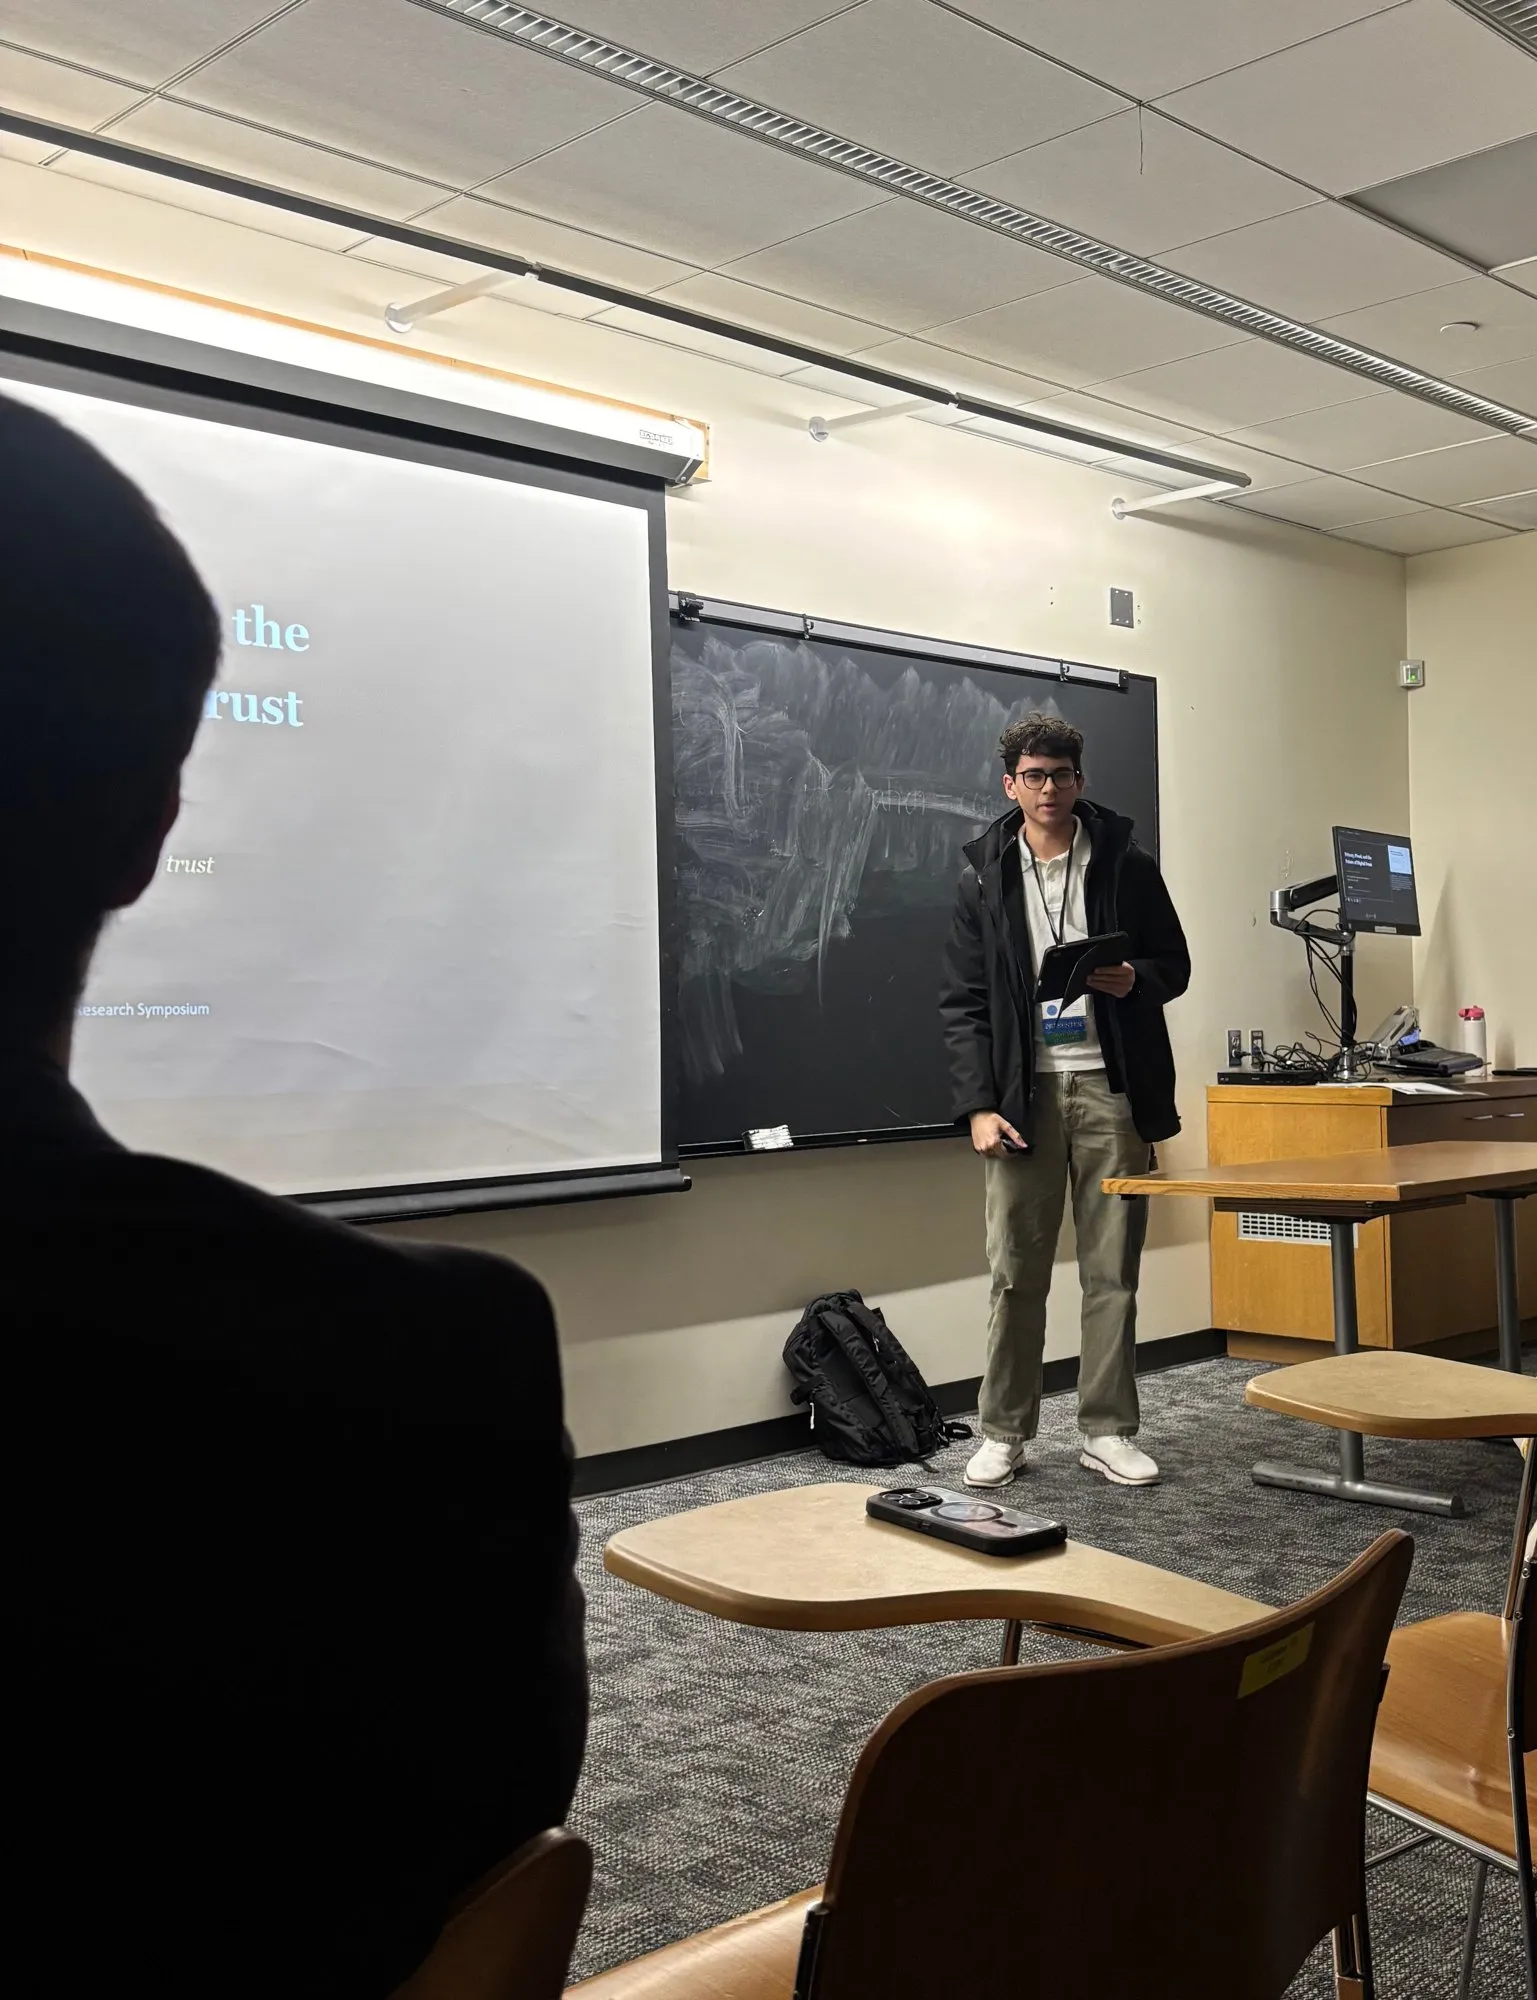
Presenting at the Macksey Symposium.
The idea
The whole framework is built to let you prove the one thing a site needs to know about you, like being over 18, without handing over who you are. It follows three principles:
- Minimum disclosure: share only the answer and leave the data behind it where it is.
- Unlinkability: nobody should be able to tie your age check on one site to your age check on another.
- Proportionality: use the least intrusive check that works, and move up only when you actually need to.
How it works
The everyday version is a wristband at a venue: you’ve been checked at the door, so the bar doesn’t need to see your license again. It just needs to know that someone trustworthy already checked.
The framework breaks that down into four steps:
- The site asks a narrow question that doesn’t identify you, like “is this person over 18 this week?”
- The question is sealed so it can’t be read or changed on the way.
- A separate authority that can actually vouch for your age returns a one-time yes or no proof.
- The site checks that proof against the question it asked, and that’s all it gets.
For me, the most important part is that nobody ends up holding the whole picture. The site gets only the answer, with nothing along the way tying that answer back to who you are.
The design uses existing internet standards throughout, with blind signatures from the IETF’s Privacy Pass work for the proof. By default, it starts with the least invasive option, like an estimate done on your own device. Only when that isn’t enough does it move up to a stronger check using selective-disclosure credentials (SD-JWT and W3C Verifiable Credentials), which can show “over 18” without showing your birthdate.
A couple of details matter more than they might seem to. The proof includes a hash of the rule being checked, for example “over 18, valid for this week,” so a proof issued for one question can’t be reused to answer a different one. The design also bans the things that usually make people trackable: session IDs, precise timestamps and anything unique to one user.
Less than one bit
I also wanted a way to actually measure how much information a check gives away about you. If about 80% of people are eligible, a yes or no check reveals about 0.72 bits of information on average. Uploading a full ID, on the other hand, gives away hundreds of bits.
What it doesn’t solve
I’d rather be upfront: this doesn’t solve everything.
- Services can still link some checks together if they collude or use browser fingerprinting or timing to match people up.
- The authorities that would vouch for people don’t yet exist everywhere, and on-device age estimates vary in accuracy.
- Before regulators will trust all of this, they need to be able to audit and accredit it.
- It can’t stop a government that actually wants the data, but it does make it a lot harder to claim the data was technically necessary.
Since the talk, I’ve also started thinking the biggest gap is honestly on the other side: whoever asks for the data has to be held to asking for the minimum, or minimum disclosure doesn’t work. That’s where the paper I wrote after the talk ended up going.